Under 1% phish-click rate after six months on Phishfirewall's rebuilt simulation SaaS
Phishfirewall's security-awareness product rebuilt from no-code into a SaaS with a mailer, back office and API on Node.js, React and Google Cloud.
- phish-click rate guaranteed after six months of training
- < 1%
- phish-click rate of competing products after six months
- > 5%
- send cycle for simulation and training emails
- 3 min
- sync cycle for opens and clicks from Pardot
- 10 min
Context
Erbis built a full-featured product that prevents phishing attacks by training employees. Below are the project details, the challenges, the technologies and the business outcome.
Challenge
Phishfirewall, an established security-awareness software provider, chose Erbis to enhance a product that prevents phishing through employee education. The client already had a solution on a no-code platform, but it had significant operational limitations. We proposed building a classic SaaS with a high-code approach; the client agreed and work began.
One challenge was migrating data from the existing platform to the new high-code framework. Another was building a system that adapts quickly to new types of phishing: attackers evolve as fast as the technology, so an anti-phishing training system must keep supplying users with current data and updates.
Pre-development
We started by studying the existing platform and the project’s technical documentation. Our business analyst interviewed the client to establish goals, understand the target audience and draw up a roadmap. This analysis identified the key pain points in the existing solution and prioritized the features most critical to educating users about phishing.
Three full-stack developers were assigned, working under our CTO, who set the technology strategy and stayed in direct contact with the client. Transparent communication kept both sides aligned throughout, with no misunderstandings or conflicts.
Solution
We combined low-code and high-code tools to deliver quickly and efficiently. The team built three components: the Mailer, the back office and a proprietary API.
Mailer. Sends emails to the customer’s employees through Pardot (Salesforce) Mailer. It synchronizes segments, users and email templates from Pardot into the application database and selects each day’s potential recipients of phishing emails. Front end in Retool (low-code); back end in Node.js and Express.js with PostgreSQL; deployed to Google Cloud with Docker.
Back office. The administrative hub where users manage every aspect of the application. Front end in React with Chart.js and MUI; back end in Node.js with Express, Axios, Passport, Sequelize and Stripe; integrated with the Taiga API to create phish reports.
API. Lets users work with their company data, mailing history, user actions, phishing reports and more.
Because the project was relatively small with a predictable feature set, we chose a waterfall lifecycle: each phase gathered requirements, then developed, tested and deployed a set of functionality before the next phase began.
End product
The Phishfirewall application raises users’ awareness of different phishing attacks and so reduces data leaks and financial losses for the organization.
Every 3 minutes the application selects potential recipients and sends emails. The email flows are:
- Introduction. Introductory information and the user’s choice of a key phrase
- Phishing. Simulated phishing emails
- Training. Training emails
- Mixed. A combination of training and phishing
- Administrative. Announcements for back-office administrators
Every 10 minutes, user actions (opens and clicks) are pulled from the Pardot API. If a user clicks a link in a phishing email it is recorded as a click and a warning email alerts the user to the danger. If the user does not click within a set period, they receive a congratulatory email. All opens and clicks are stored in the database, and on the first day of each month per-user statistics are updated and sent to Pardot.
Architecture and tech stack
A Node.js and Express.js back end on PostgreSQL runs on Google Cloud in Docker containers. The Mailer’s admin front end is built in Retool; the back office is a React application; and integrations connect to Pardot for email delivery and engagement data, Taiga for phish reports and Stripe for billing.
- Node.js and Express.js
- React, Chart.js and MUI
- PostgreSQL with Sequelize
- Retool
- Docker on Google Cloud
- Pardot (Salesforce) API, Taiga API, Stripe
Results
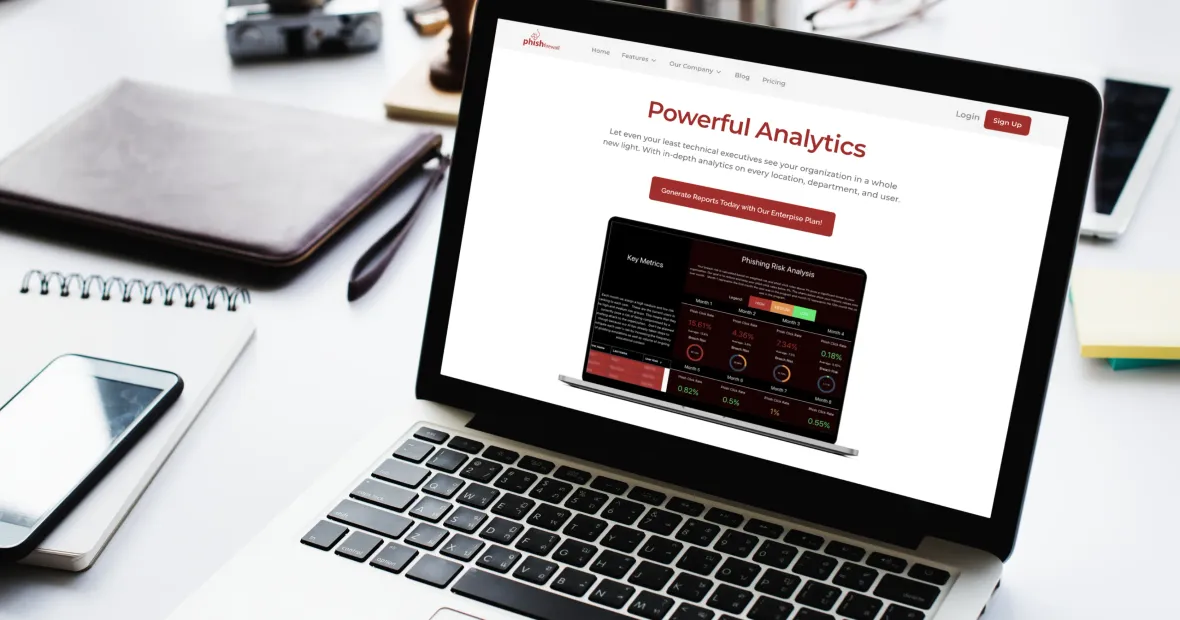
With the application, our client guarantees its customers a phish-click rate below 1% after six months. Competing products still show a click rate above 5% after six months.
Further benefits of the software:
- Increased employee engagement
- Reduced phishing vulnerabilities
- A stronger cybersecurity culture
What made it work
Erbis’s takeaways from this engagement:
- Use low-code where the audience is internal. Retool for the mailer admin saved build time without compromising the customer-facing product.
- Treat the email platform as a data source, not just a sender. Pulling opens and clicks back from Pardot is what makes the training loop measurable.
- Fixed scope earns a fixed process. Waterfall was the right choice here because the feature set was small and predictable; it is not our default.
- Close the loop with the user immediately. A warning on a click and a congratulation on restraint turn a simulation into training.